
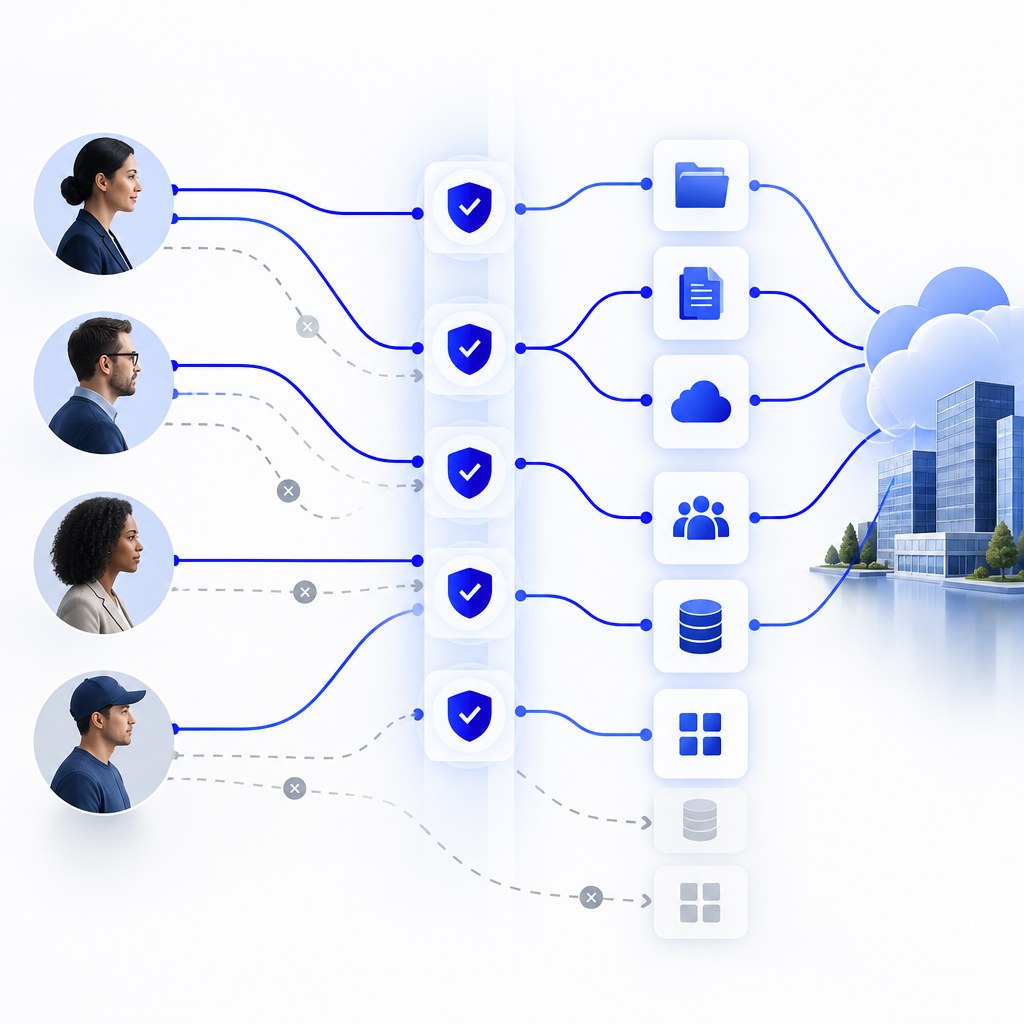
Executive takeaway: Microsoft 365 access governance is the discipline of ensuring that the right people and applications have the right access for the right amount of time. Multifactor authentication helps verify who is signing in. Access governance answers a different question: should that person, vendor, or application still have access at all? For business leaders, the stakes are financial exposure, customer information, operational continuity, and accountability.
Consider a familiar situation. Your company engages an outside consultant for a six-week project. To collaborate, an employee invites the consultant into Microsoft Teams and shares a collection of files in SharePoint. The engagement ends, the invoice is paid, and everyone moves on. Six months later, who has verified that the consultant’s access was removed?
The consultant may have done nothing wrong. That is precisely the point: access that outlives its business purpose is a control failure even when no incident has occurred. Over time, a business can accumulate access paths that nobody deliberately approved for continued use.
What is Microsoft 365 access governance?
Microsoft 365 access governance is the set of policies and operating procedures used to request, approve, review, change, monitor, and remove access to company information and cloud services. It includes employees, contractors, external guests, administrators, and connected applications. Microsoft Entra ID provides identity and access controls for Microsoft 365, while Teams, SharePoint, Exchange, and other services have their own permissions and sharing configurations.
Good governance connects a technical permission to a business reason and a responsible owner. It should be possible to answer four questions about sensitive access: Who has it? Why do they need it? Who approved it? When will it be reviewed or removed?
That is different from the credential-theft problem discussed in our earlier article, Credential Theft: The Business Risk Hiding Behind a Valid Login. There, the concern is an attacker misusing a legitimate identity. Here, the concern is whether legitimate identities and applications have accumulated access the business no longer intends to grant.
Where do organizations lose control of Microsoft 365 permissions?
1. Departing employees and role changes leave unfinished business
An employee who moves from finance to operations may retain access to financial reporting folders, shared mailboxes, or administrative groups. A departing employee may have Microsoft 365 sign-in disabled while a separate SaaS account, shared credential, or application session remains active.
Business consequence: The organization carries avoidable access to confidential information and may struggle to demonstrate that offboarding was completed. A reliable joiner-mover-leaver process needs an HR trigger, an IT execution checklist, a business owner for exceptional access, and evidence that each critical system was addressed.
Microsoft notes that revoking Entra sign-in and refresh tokens does not necessarily end sessions issued independently by connected applications. That is why offboarding should verify application-level deprovisioning, rather than stop at disabling one account. Microsoft: Revoke user access in Entra ID.
2. Guest access grows faster than anyone reviews it
Guest collaboration is a legitimate business need. Clients, auditors, architects, outside counsel, accountants, and contractors may require temporary access to Teams, SharePoint sites, or documents. Problems arise when projects have no expiry dates or the person responsible for the guest’s access leaves the company.
Business consequence: Sensitive projects may remain accessible to external parties long after the original purpose ends. Assign a business sponsor to each external relationship, review guest permissions on a recurring schedule, and remove access when the engagement closes. Microsoft specifically recommends reviewing and cleaning up external identities that are no longer needed. Microsoft: Review external users.
3. Administrator privileges become permanent by default
Someone may receive elevated Microsoft 365 permissions to resolve an urgent issue, configure a service, or help with a migration. If the organization does not revisit that assignment, temporary authority can become permanent. Broad administrative access deserves special attention because it may allow changes to security settings, accounts, mailboxes, and other critical resources.
Business consequence: One inappropriate or compromised privileged account can affect far more than one employee’s files. Use the least-privilege principle, separate ordinary work from administrative activity where appropriate, and review privileged roles routinely. Document and test emergency administrative access so a security control does not accidentally lock the business out of its own environment. Microsoft’s guidance calls for carefully secured emergency-access accounts and regular validation of their availability. Microsoft: Emergency access accounts.
4. Connected applications inherit permissions that outlive their usefulness
A productivity add-on, reporting service, or workflow integration may request permission to read mail, files, or directory information. Some permissions are granted on behalf of one user; others may be approved more broadly. Even if the original employee or project is gone, the integration may remain.
Business consequence: Data access can continue through an overlooked application rather than a familiar employee login. Maintain an inventory of authorized integrations, record their owners and business purposes, evaluate requested permissions, and revoke grants that are no longer necessary. Microsoft documents how administrators can review enterprise-application permissions and revoke unnecessary grants. Microsoft: Review application permissions.
5. Security policies exist, but exceptions are not governed
Access rules may require additional verification, a compliant device, or other conditions. These controls are valuable, but broad exclusions and poorly documented exceptions can undermine their intent. Equally, a sudden policy change made without testing can disrupt legitimate operations.
Business consequence: The business either carries exceptions that no one owns or experiences avoidable downtime from rushed changes. Require a business justification, named approver, expiration or review date, and a tested rollback plan for material exceptions.
What should an effective Microsoft 365 access governance program include?
- Ownership: Assign business owners to sensitive information, major SharePoint sites, critical applications, and privileged permissions. IT manages controls; business leaders decide which access is justified.
- Lifecycle procedures: Tie onboarding, job changes, and departures to standardized access actions, including external applications and devices where relevant.
- Periodic attestation: Ask information owners to confirm that each important permission remains necessary. Record approvals, removals, exceptions, and follow-up actions.
- Least privilege: Favor narrowly scoped roles and time-limited elevated access where the technical platform and licensing support them.
- Application and guest oversight: Keep current lists of external collaborators, service principals, integrations, sponsors, and business purposes.
- Monitoring and response: Review unusual privilege assignments, significant sharing changes, and suspicious access activity; ensure alerts reach a responsible person who can investigate and act.
- Evidence and testing: Measure whether access is removed when promised and whether emergency procedures work in practice.
This approach is consistent with the NIST Cybersecurity Framework 2.0, which emphasizes governance alongside identifying, protecting, detecting, responding, and recovering. The framework provides a management structure; it does not substitute for validating individual technical configurations.
Can a business start without buying another Microsoft security license?
Yes. The first step is an access inventory and an accountable review process, not a software purchase. An organization can assign owners, examine existing users and privileges, review external sharing, and document deprovisioning tasks before introducing automated governance tooling.
For organizations with Microsoft 365 Business Premium, Microsoft Entra ID P1 is included, enabling Conditional Access capabilities when properly licensed and configured. However, Microsoft Entra’s automated Access Reviews feature generally requires qualifying P2 or Entra ID Governance licensing; advanced governance and risk-based capabilities have separate licensing requirements. A manual, documented permission review is not the same as the licensed Access Reviews product. Confirm the exact features and license assignments before promising a capability or activating a policy. See Microsoft Entra licensing and Access Reviews requirements.
This distinction matters to executives: governance is a business practice supported by technology, not a feature that appears automatically because an organization owns a premium subscription.
A practical 30-day Microsoft 365 access review for leadership
Rather than demand an immediate overhaul, begin with a focused review of the accounts, data, and applications that could create the most serious business harm.
- Week 1 — Establish scope and ownership. Identify high-impact Teams and SharePoint locations, privileged administrator roles, finance and executive identities, external guests, and connected applications. Name the business owner for each area.
- Week 2 — Verify necessity. Compare active employee and contractor records with access assignments. Ask owners to approve, narrow, or remove permissions. Give temporary exceptions an expiration or next-review date.
- Week 3 — Remediate and protect. Remove obsolete access, reduce unnecessary privileges, review application permissions and external sharing, and test that valid business workflows still function. Changes affecting access to critical systems should be coordinated to avoid disruption.
- Week 4 — Test the process. Run a sample offboarding exercise, verify how quickly access is revoked across Microsoft 365 and connected applications, review logging and escalation, and publish an exceptions register with owners and deadlines.
Do not confuse a completed spreadsheet with a completed control. The value comes from closing the gaps found and repeating the review when personnel, vendors, systems, or business needs change.
Which access governance metrics should executives request?
A useful management report should show trends, exceptions, and accountable owners rather than a reassuring total number of accounts. Consider:
- Offboarding completion: Percentage of employee and contractor departures whose critical access was revoked within the organization’s documented target.
- Unowned permissions: Number of sensitive access grants, privileged roles, and connected applications lacking a current business owner.
- External access currency: Percentage of guest accounts with a named sponsor and current review date.
- Review remediation: Number of permissions flagged for removal, how many were corrected, and how many remain overdue.
- Exception age: Number and age of temporary access-policy exceptions, with a named approver and expiration date.
Targets should reflect the value of the information and the operational impact of delays. The question for a CEO, CFO, or board is not whether a dashboard is green. It is whether the organization can demonstrate that access is appropriate today.
Where Ntreks fits: managed security tied to business accountability
Ntreks approaches Microsoft 365 security through the business problems it must solve: limiting unnecessary exposure, strengthening operational visibility, maintaining continuity, and making incident decisions faster and more reliable. Our managed security services work can help organizations assess identity and access practices, evaluate licensing and configuration, coordinate monitoring and response, and improve the procedures that connect IT with leadership, human resources, and department owners.
We also look for opportunities to simplify overlapping tools and fragmented responsibilities. Strong governance should not require your executives to navigate five consoles to find one accountable answer. Learn more about our cybersecurity services, compliance and governance support, and approach to reducing security tool sprawl.
Frequently asked questions about Microsoft 365 access governance
Does MFA solve Microsoft 365 access governance?
No. MFA helps verify a person’s identity during sign-in. Access governance determines which people and applications should have access, for what purpose, and when that access must change or end.
Should a company remove all external guests from Microsoft 365?
No. External collaboration is often essential. The goal is to give approved guests only the access they need, assign a business sponsor, and review or remove access when the engagement ends.
How often should Microsoft 365 access be reviewed?
Review promptly after job changes, departures, vendor transitions, and major permission changes. Perform recurring risk-based reviews of sensitive data, privileged roles, and external access; the schedule should match the organization’s risk and compliance needs.
Is Microsoft 365 Business Premium enough for access reviews?
Business Premium includes Entra ID P1 and Conditional Access capabilities, but Microsoft’s automated Entra Access Reviews product generally requires additional qualifying licenses. Organizations can still conduct manual access reviews with documented ownership and evidence.
Who owns access governance: IT, HR, or the business?
All three have distinct responsibilities. HR supplies authoritative personnel changes, business leaders approve the need for access, and IT or the security provider implements, monitors, and verifies controls. Leadership is accountable for the overall process.
Executive next step: Ask your team for a list of your most sensitive Microsoft 365 permissions, who owns each one, and when it was last reviewed. If that answer is difficult to produce, contact Ntreks to discuss a Microsoft 365 security and access governance review. We will start with business exposure and operational outcomes, not a shopping list of software.